A Guide to Security Threats to a Network for Indiana Businesses
TL;DR: Your Instant Security Briefing
- Threats Are Business Problems: Security threats like malware, ransomware, and phishing aren't just IT issues; they directly cause downtime, which can cost up to $9,000 per minute and cripple your business.
- Local Risks Are Real: Aging server hardware in a Greenwood business park or spotty Wi-Fi in a downtown Indy building are common entry points for attackers.
- Proactive Defense is ROI: A managed security approach using tools like Bitdefender GravityZone and immutable off-site backups prevents costly emergencies, converting "wasted tech time" into a predictable monthly budget and billable hours.
- Compliance is Critical: For Indiana businesses in healthcare or defense, meeting standards like HIPAA and CMMC is non-negotiable. A breach can lead to massive fines and lost contracts.
- Actionable Steps: Implementing a Zero Trust architecture, mandatory multi-factor authentication, and getting a professional network audit are the first steps to securing your operations.
When you hear about "security threats to a network," your mind might jump to things like ransomware locking up your files or sneaky phishing emails trying to steal your passwords. And you'd be right. These attacks are designed to cause chaos, swipe your data, and hit your business where it hurts—your wallet.
Why Network Security Is Really Just Business Continuity
For a lot of Johnson County business owners, "cybersecurity" can feel like a big, fuzzy, technical term. It's something you assume is a problem for the big downtown Indy tech hubs, not for your company. But after 17 years of local service, we've seen firsthand how one security slip-up can bring a growing company to its knees.
Think about that server humming away in the closet of a business park in Greenwood. If it’s old, it’s not just slow—it’s a massive security hole. Every minute an employee stares at a loading screen is "wasted tech time" that could've been spent on billable work. Worse, that unpatched, outdated system is basically a welcome mat for an attacker.
Shifting From Reactive To Proactive Defense
A security breach isn't just an IT problem; it's a direct assault on your ROI. When your network goes down, the costs can skyrocket to over $9,000 per minute. Suddenly, a preventable issue becomes a financial disaster. This is exactly where a managed approach to IT security flips the script. Instead of just reacting to fires, we build a firewall to prevent them from starting.
The goal isn’t just to fix problems—it’s to create an environment where those problems are far less likely to happen. This means predictable monthly budgets for security instead of unpredictable, sky-high bills for emergency recovery.
To get past the vague fears and build a real-deal defense plan, you need to know what you’re up against. Using a solid cybersecurity risk assessment template is the perfect first step. It turns that foggy uncertainty into a clear, actionable strategy.
For our clients, this means putting solutions in place that actually fit their business. A local healthcare provider needs to know their network is ironclad for HIPAA compliance. A defense contractor over on the I-65 corridor has to meet tough CMMC standards. Our deep experience with these rules ensures your security is not only strong but also fully compliant.
You can learn more about the fundamentals in our guide on the top network security best practices for Indianapolis businesses. This guide dives into the most common security threats to a network and shows you how to fight back.
Stop leaving your business exposed. A secure network is the bedrock of modern business continuity. It’s time to find out where you’re vulnerable.
Meet the Digital Saboteurs: Malware, Ransomware, and Phishing
Let's pull back the curtain on the most common digital enemies gunning for your business. When people talk about security threats to a network, they often just say "viruses." The reality is a whole lot scarier and more specific. We're dealing with sophisticated tools built to steal your data, grind your operations to a halt, and bleed your bank account dry.
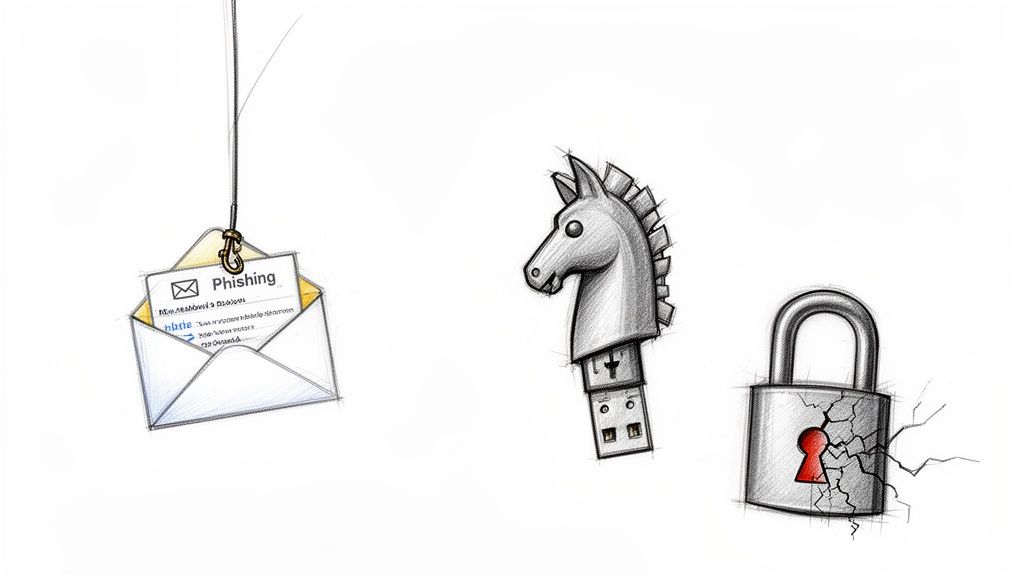
As a Johnson County business owner, you need to know exactly what you're up against. Understanding the enemy is the very first step in building a defense that actually works and protects your hard-earned success.
Malware: The Uninvited Guest in Your System
Malware is just short for "malicious software," and it’s the catch-all name for any nasty code designed to cause trouble. It isn't one single thing; it's a whole army of digital pests, and each one has a different mission.
Think of it like a squatter who won't leave your office. Some of them quietly rifle through your file cabinets looking for secrets (spyware), while others make a copy of your front door key so they can let their friends in later (trojans).
Here are a few of the usual suspects we see bothering businesses across Central Indiana:
- Spyware: This sneaky bit of code hides on a computer and secretly logs what you do, grabbing passwords, credit card numbers, and confidential business plans.
- Trojans: Just like the mythical Trojan Horse, this malware pretends to be a useful program. Once you let it inside, it swings open a backdoor for attackers to waltz in and take control.
- Adware: It might not be as destructive, but adware can hijack your web browser with a non-stop barrage of pop-ups, slowing your team down and killing productivity with endless distractions.
We use advanced endpoint protection tools like Bitdefender GravityZone to act as a digital bouncer, identifying and kicking these threats out before they ever get past the velvet rope.
Ransomware: Your Business Data Held Hostage
Of all the security threats out there, ransomware might just be the most terrifying. Seriously. Imagine a hijacker walking into your office, super-gluing every single file cabinet shut, and then demanding a fortune for the keys. That's exactly what ransomware does to your digital files.
This type of malware encrypts everything—client records, financial documents, project files—making it all completely unusable. The attackers then demand a massive ransom, usually in cryptocurrency, to give you back your own data.
Paying the ransom is a huge gamble. There's zero guarantee you'll get your data back, and it basically paints a giant target on your back for future attacks. In our 17 years of local service, we've seen the aftermath, and it’s absolutely devastating.
The only real escape plan is a rock-solid backup strategy. We set up immutable off-site backups for our clients, which means we create tamper-proof copies of your data that even ransomware can't touch. This way, you can restore your operations fast without paying a single cent to a criminal. To dive deeper, check out our guide on how to prevent ransomware attacks on your Indiana business.
Phishing: The Art of Digital Deception
Phishing attacks are a masterclass in manipulation. These aren't lazy, typo-filled emails anymore. Criminals now craft messages that look incredibly real—a fraud alert from your downtown Indy bank, a shipping confirmation from a key supplier, or even an urgent request from your own CEO.
Their whole game is to trick you or an employee into doing something you shouldn't:
- Clicking a malicious link that installs malware.
- Entering login credentials on a picture-perfect fake website.
- Wiring company funds directly to a fraudulent account.
For our healthcare clients, one wrong click can trigger a massive HIPAA data breach, leading to six-figure fines and a total loss of patient trust. For the defense contractors we work with along the I-65 corridor, it could mean compromising sensitive data and failing a critical CMMC audit.
The best defense is a one-two punch of technology and training. We use smart email filtering that catches and quarantines suspicious messages, but we also provide ongoing security awareness training to turn your team into a human firewall that can spot a phish from a mile away.
When the Threat Comes from Inside Your Walls
It’s easy to picture network threats as shadowy hackers hunched over a keyboard in some far-off country. But honestly? Some of the most devastating vulnerabilities are already inside your building, walking your hallways.
We're talking about insider threats and network misconfigurations—the kind of stuff created by the very people you trust or by simple, overlooked mistakes in your IT setup. They can be just as costly, if not more so, than a full-blown cyberattack.
Just ask a rapidly growing company we once helped in Hamilton County. A well-meaning employee, just trying to make remote access easier for their team, set a painfully simple password on their main UniFi networking controller. It took a matter of hours for an automated bot to scan their network, guess the password, and seize complete control.
The downtime from that one little mistake cost them tens of thousands in lost business. That’s a classic, unintentional insider threat—no malice, just a simple slip-up with catastrophic consequences.
The Two Faces of Insider Threats
Insider threats aren't always about a disgruntled employee sneaking out the door with a hard drive full of secrets, though that definitely happens. More often, they’re completely accidental. Knowing the difference is crucial for building a defense that actually works for your Central Indiana business.
You really only need to watch for two main types:
- The Accidental Insider: This is, by far, your most common risk. It’s the team member who unknowingly clicks a phishing link, uses a weak password like "Summer2024!", or plugs a sketchy personal USB drive into their work computer. They aren't trying to cause harm, but their actions swing the door wide open for an attack.
- The Malicious Insider: This one is rarer but way more dangerous. It’s a current or former employee who deliberately abuses their authorized access to steal sensitive data, mess with operations, or flat-out sabotage systems for personal gain or revenge.
Both can waltz right past your expensive firewalls because they operate from a position of trust. This is exactly why we build a Zero Trust architecture for our clients.
A Zero Trust model runs on a simple but powerful principle: never trust, always verify. It means no user or device is trusted by default, even if they’re already inside your network. Every single access request has to be authenticated and authorized before it gets the green light.
Network Misconfigurations: The Unlocked Back Door
If an insider threat is like someone accidentally leaving the front door key under the mat, a network misconfiguration is like finding out the builders forgot to install locks on the back door entirely. It's a fundamental weakness just waiting for an attacker to find it.
These are technical oversights that create gaping security holes. A common issue we see in older brick buildings around downtown Indy is improperly configured Wi-Fi, leaving the entire business network exposed. Another big one is failing to update the firmware on routers and switches, which leaves well-known vulnerabilities unpatched and ready for exploitation.
To fight this, you need a proactive game plan. Our guide on data loss prevention best practices dives into more specific steps you can take right now.
When you start treating every part of your network as potentially hostile—even the stuff behind your firewall—you create a much tougher, more resilient environment. This mindset shifts your IT from a chaotic, reactive mess into a predictable, protected asset, securing your network from the inside out and preventing the kind of downtime that can sink a growing business.
Your team is your greatest asset, but let's face it, human error is inevitable. Let's make sure a simple mistake doesn't turn into a business-ending catastrophe. We offer a Security Risk Audit for businesses in the Greenwood/Indianapolis area to pinpoint these internal vulnerabilities before anyone else does.
Understanding the Heavy Hitters: Sophisticated Cyberattacks on Your Network
Alright, let's move beyond the everyday digital annoyances. We're talking about the big, orchestrated attacks—the kind designed for maximum chaos and disruption. These are the heavy hitters, the digital equivalent of a coordinated siege on your business. For any company growing along the I-65 corridor, getting a handle on these advanced security threats to a network isn't just a good idea; it's a matter of survival.
These aren't your run-of-the-mill, random attacks. They're calculated assaults aimed squarely at your core infrastructure. The attackers behind them are patient, often well-funded, and they love to turn the very tools you rely on against you.
DDoS Attacks: The Digital Traffic Jam From Hell
Picture this: you own a popular storefront in Greenwood, and suddenly a thousand phantom delivery trucks show up, blocking every road, driveway, and parking spot. No real customers can get through. Your own staff is stuck. Business grinds to a dead halt. That's a Distributed Denial-of-Service (DDoS) attack in a nutshell.
In the digital world, hackers use a network of hijacked computers (a "botnet") to bombard your network server with an insane amount of junk traffic. Your server gets so bogged down trying to sort through the garbage requests that it can't respond to legitimate customers trying to access your site.
The result? A complete shutdown of your website, customer portals, or online services. For any business that operates online, that means instant downtime, bleeding revenue, and a major blow to your hard-earned reputation.
We've personally seen Johnson County businesses get knocked completely offline for hours by these attacks. The goal isn't always theft; sometimes it's pure, unadulterated disruption, designed to cripple your operations or act as a smokescreen for another, sneakier attack.
Zero-Day Exploits: The Boogeyman in Your Software
A Zero-Day exploit is the thing that keeps IT pros up at night. It's an attack that targets a security flaw in a piece of software that is so new, the software developer doesn't even know it exists yet. There’s no patch, no update, and no off-the-shelf fix because, as far as the good guys are concerned, the hole isn't there.
This is what makes them so terrifyingly effective. Attackers find these hidden cracks in the everyday software you use—your operating system, your web browser, you name it—and waltz right past your standard security measures.
Since you can't patch a vulnerability that hasn't been discovered, the only real defense is relentless vigilance. This is exactly why proactive monitoring through a service like our SOC-as-a-Service (Security Operations Center) is no longer a luxury. Our team provides 24/7 watch, looking for the weird, unusual behavior that often signals a Zero-Day attack in progress. That lets us isolate the threat before it causes catastrophic damage. To get a better feel for our process, take a look at our guide on the best practices for network monitoring your Indiana business needs.
Supply-Chain Attacks: When Trust Becomes a Weapon
A supply-chain attack is one of the most insidious threats out there. Instead of coming at you head-on, criminals go after a trusted third-party software vendor you rely on. They sneak malicious code into a legitimate software update, which then gets pushed out to you and hundreds—or thousands—of other customers.
You dutifully install the update, thinking you're making things more secure, but you’ve just rolled out the red carpet for the attacker. For businesses like defense contractors facing strict CMMC compliance, the integrity of your software supply chain is everything. A single compromised vendor can trigger a compliance failure and jeopardize critical government contracts.
Recent industry reports confirm this scary trend, showing that network edges and third-party services are now prime targets. In fact, vulnerability attacks now account for 20% of initial access methods, with a jaw-dropping 8x year-over-year spike in compromises of edge and VPN devices. If you want to dive deeper into the data, you can read the full Global Cybersecurity Outlook report from the World Economic Forum.
This is where true, high-level expertise makes a difference. By implementing advanced strategies like a Zero Trust architecture and deploying latency-optimized mesh nodes, we build a network that is resilient by its very design. We make sure your systems can perform reliably, even when the software you depend on can't be fully trusted.
Don’t wait for one of these sophisticated attacks to test your defenses. We offer a Security Risk Audit specifically for businesses in the Greenwood and Indianapolis area to find these advanced threats before they find you.
The Financial Fallout of Modern Network Threats
Every single device plugged into your network is a potential doorway for an attacker. We're not just talking about servers and computers anymore.
Think about the smart security cameras at your Fishers office, the networked machinery in a Plainfield warehouse, or even the smart thermostat in the breakroom. Each one is an Internet of Things (IoT) device, and each one adds another potential entry point for the bad guys.
We’ve covered the "what"—malware, phishing, and even those sneaky supply-chain attacks. Now, let’s talk about the "so what?" and connect every one of those threats directly to your bottom line. We’re moving past hypotheticals and breaking down the real-world, dollars-and-cents cost of a breach for an Indiana SMB.
More Than Just a Ransom Payment
When a business in Johnson County gets hit with a cyberattack, the ransom demand that pops up on the screen is often just the opening act. The true financial damage is a chaotic, sprawling mess of direct and indirect costs that can absolutely cripple a growing company.
It’s a nasty domino effect. A breach can lead to:
- Crippling Downtime: Every minute your network is down, you’re bleeding money. With downtime costs soaring up to $9,000 per minute, even a few hours offline can be a financial knockout punch.
- Steep Regulatory Fines: For our clients in healthcare, a breach exposing patient data can trigger massive HIPAA fines. For defense contractors, failing a CMMC audit after a security lapse can mean losing huge contracts.
- Exorbitant Recovery Costs: Think emergency IT services, forensic investigators trying to piece together how the attackers got in, and the sky-high cost of rebuilding systems from scratch. It’s a staggering, unplanned expense.
The image below gives you a peek into how these attackers are getting in. They’re exploiting vulnerabilities and compromising devices on the fringes of your network.
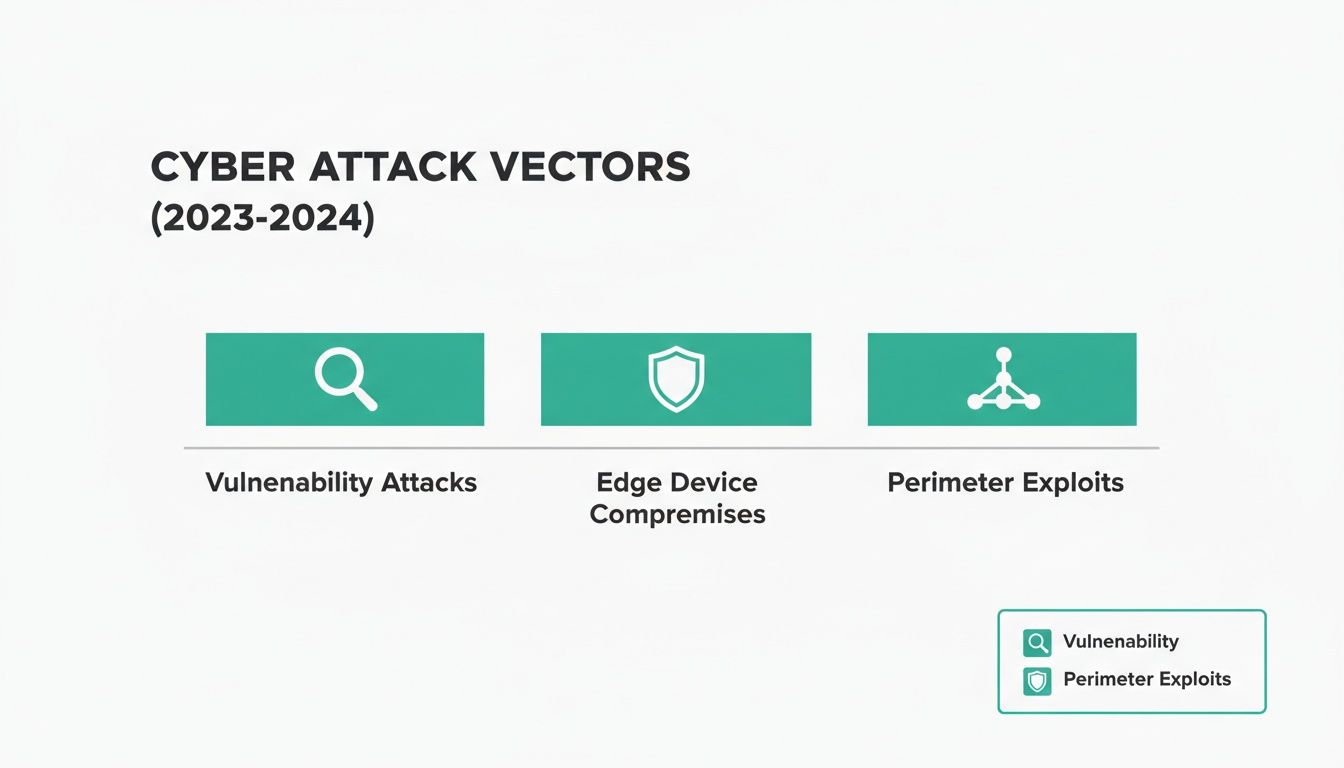
What this shows is a clear pattern: attackers go for the low-hanging fruit. They are actively targeting the weakest points—unpatched software and poorly secured network devices—to get their foot in the door.
The Long-Term Damage to Your Reputation
Beyond the immediate hit to your bank account, the long-term impact is often about regaining trust after a data breach. When customers and partners find out their sensitive data was compromised while in your care, that trust evaporates. Rebuilding it is a long, expensive, and sometimes impossible journey.
The global numbers are frankly staggering. Cybercrime is projected to cost the world $10.5 trillion annually. In the U.S., data breaches now average a jaw-dropping $10.22 million each. While your business might not face a bill that high, consider this: ransomware alone now accounts for 51% of all cyberattack costs for small and medium-sized businesses. And that number keeps climbing.
Real Costs of a Network Breach vs Proactive Managed Security
It’s easy to think of managed security as just another line item on the budget. But when you stack it up against the potential cost of a disaster, the math becomes crystal clear.
| Expense Category | Cost After a Breach (One-Time, Unplanned) | Managed Security Investment (Monthly, Predictable) |
|---|---|---|
| Downtime & Lost Revenue | $1,000s - $100,000s+ (Potentially business-ending) | Included (Proactive monitoring minimizes downtime risk) |
| Forensic Investigation | $15,000 - $50,000+ | $0 (Included in comprehensive plans) |
| System Restoration | $10,000 - $100,000+ (Depending on complexity) | Included (Robust backup and recovery systems) |
| Regulatory Fines (HIPAA, CMMC) | $50,000 - $1.5 Million per violation | Included (Compliance management and reporting) |
| Reputation Damage & Customer Loss | Incalculable | Minimized (Strong security builds customer trust) |
| Legal Fees & Lawsuits | $20,000 - $200,000+ | Reduced Risk (Proper protocols limit liability) |
| Ransom Payment | $50,000 - $2 Million+ (With no guarantee of data return) | Near-zero risk (Multi-layered defense prevents intrusion) |
As you can see, the choice is between absorbing a chaotic, unpredictable financial bomb and making a smart, predictable investment in your stability.
Proactive security converts "wasted tech time" and emergency spending into a stable, predictable operational expense that protects your ROI instead of decimating it. Our guide on how to protect against phishing attacks dives deep into the direct ROI of stopping just one of these common threats.
Don’t wait until you're staring at a ransom note to think about your network's security. It's time to understand your specific risks and build a defense that protects your finances, your reputation, and your future.
Your Action Plan for a Resilient and Secure Network
Knowing what a ransomware attack is feels very different from knowing what to do when one hits. It’s time to stop worrying and start building. For businesses here in Greenwood and across the Indianapolis metro, a strong network isn't just an IT issue—it's the bedrock of your business.
This isn’t about buying some magic piece of software and calling it a day. Real security is about layering smart, strategic defenses that shut down the loopholes criminals love to wiggle through. A solid plan transforms your network from a potential disaster zone into a fortress, protecting your bottom line and turning what could have been downtime into productive, billable hours.
Building Your Human Firewall
The fanciest security tech on the planet can be brought to its knees by one accidental click. That's why any good security plan has to start with your people.
We champion ongoing, practical training that empowers your team to become your first line of defense. This is no stuffy, one-and-done seminar. We’re talking about teaching them how to spot the subtle, tricky red flags of a modern phishing attack and building a healthy dose of suspicion before they click any link or download any file.
Mandating a Modern Defense
Next, we bolt the digital doors. We make mandatory multi-factor authentication (MFA) non-negotiable for every critical system—email, VPN access, financial software, you name it. Think of it like needing both a key and a PIN to get into your office. Even if a cybercriminal manages to steal a password, MFA stops them dead in their tracks.
Alongside MFA, we get ruthless with patch management. Outdated software is like leaving a window wide open for intruders. Our team takes this off your plate, making sure every server, computer, and network device is constantly updated with the latest security patches. We close the vulnerabilities before they can be used against you.
In our 17 years of local service, when we dissembled a similar client’s failing RAID array after a ransomware hit, we saw firsthand how their lack of immutable off-site backups—a cornerstone of our strategy—turned a preventable problem into weeks of crippling downtime and permanent data loss.
Prioritizing the Biggest Threat
Let's be blunt: ransomware is the undisputed king of cyber threats right now, showing up in a staggering 44% of all data breaches. For small and medium-sized businesses in Indiana, it's even scarier—ransomware now accounts for 51% of the average cyberattack costs for SMEs. These crooks move fast, too, with over half of all attacks discovered within a week, long after the damage is done. You can discover more about the alarming rise of ransomware on NordLayer.
Stop guessing with your security. You wouldn't leave your office unlocked overnight, so why leave your digital front door wide open?
We invite businesses in the Greenwood and Indianapolis area to schedule a complimentary Security Risk Audit. Let's find your specific weak spots and build a practical, affordable plan to fix them—before an attacker finds them for you.
Got Questions? We’ve Got Answers.
Here are the real, no-fluff answers to the questions we hear all the time from business owners in and around Indiana. Let's clear the air on what really matters for network security.
"We're Just a Small Business. Are We Really a Target for Hackers?"
Oh, absolutely. It's a common misconception, but hackers love small businesses for one big reason: they often assume you're an easy target. They aren't hand-picking victims one by one; they're running automated scanners 24/7, looking for any open digital door. Your size doesn't make you invisible to them.
Frankly, a successful attack can be far more devastating for a small or medium-sized business that doesn't have a massive IT department or deep pockets to handle the recovery. Think of proactive security not as a big-corporation luxury, but as essential survival gear for any business in Johnson County that wants to keep its doors open.
"If I Can Only Do One Thing to Protect My Network, What Should It Be?"
This one's easy: Multi-Factor Authentication (MFA). Turn it on for everything. Right now.
Seriously. Email, your VPN for remote work, any cloud software, and especially anything tied to your finances. MFA requires a second piece of proof—like a code from your phone—before letting someone in. This single step shuts down the overwhelming majority of attacks that start with a stolen password. It's cheap, it's effective, and for our clients, it's completely non-negotiable.
"How Does a Network Assessment Actually Save Me Money?"
Think of a Network Assessment as a home inspection for your company's technology. You wouldn't buy a building without checking for a leaky roof or a cracked foundation, right? We do the same for your digital infrastructure, finding the hidden risks before they become wallet-draining disasters.
We uncover things like that one server someone forgot to update (a welcome mat for ransomware) or network bottlenecks that are secretly costing your team hours of productivity every week.
By fixing these issues before they cause a crisis, you avoid the five- or six-figure cost of a data breach and the nightmare of downtime. You're turning a potential catastrophe into a predictable, smart investment that actually makes your team more efficient. That's not a cost—that's a direct boost to your bottom line.
Stop guessing where your vulnerabilities are and start plugging the holes. Finchum Fixes IT offers a comprehensive Security Risk Audit designed specifically for businesses in the Greenwood and Indianapolis area. Let's build a defense that actually works for you.
Ready to get started? Schedule your audit with Finchum Fixes IT today.